3,998 L-BTC Minted: Why Sidechain Security Is Still the Soft Spot
The Liquid Network exploit minted 3,998 L-BTC, exposing critical sidechain security flaws. What on-chain data really says about risk and custody.
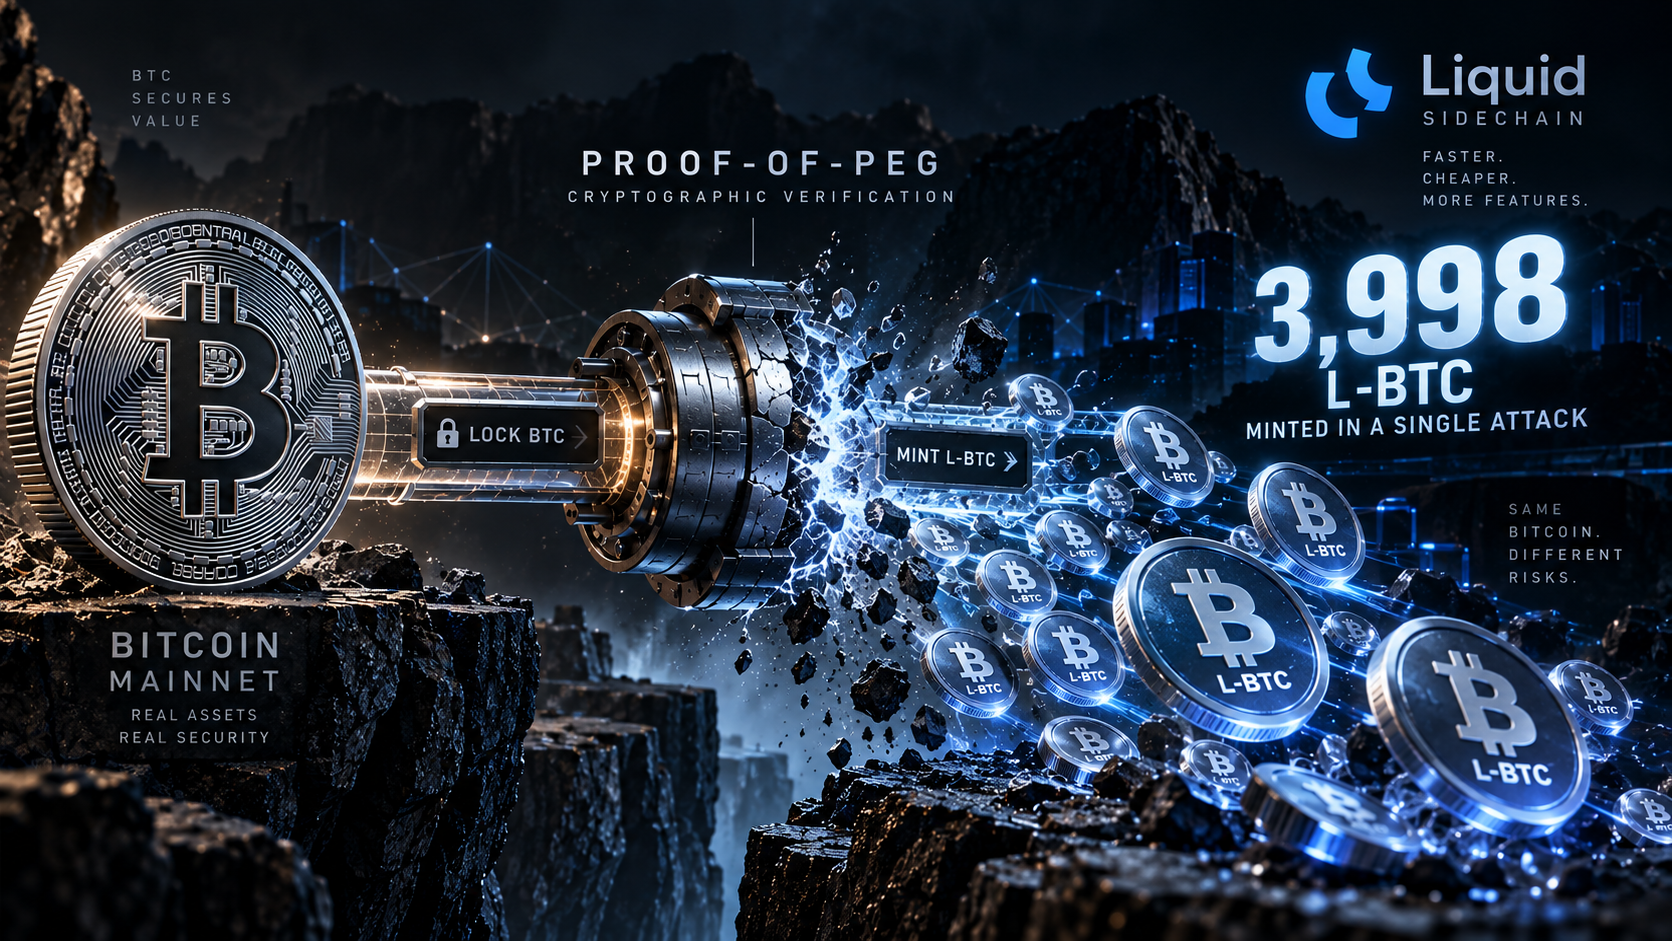
3,998 L-BTC Minted in a Single Attack
The number is 3,998. That is how much L-BTC an attacker minted in the Liquid Network exploit — the largest hack of a Bitcoin sidechain in 2026. It is a simple number, but it is not normal. Even by crypto's shifting risk standards, it is a hole big enough to demand attention.
SlowMist spelled out the technical gap: the attacker bypassed cryptographic verification, not social-engineered a hot wallet or found a config file. This is about code, not carelessness. It is one more proof that the problem with sidechains is not operational, it is architectural.
This matters for a technical reason. Sidechains are supposed to inherit the security of their base layer. The point of Liquid is to take bitcoin, lock it, and trust cryptography to ensure that L-BTC really represents BTC. If someone can mint L-BTC without the locked bitcoin on mainnet, the peg is broken. That destroys the reason to trust the ledger at all, and it is not a small inconvenience. It is the scenario that provokes the question: How much more of this risk is hiding, untested, in other chains?
Why This Breach Surprised Me
Most hacks look like endpoint failures: a single compromised server, a leaky key, or a phishing flow tricking an admin. This one did not. The attacker touched the core mechanism — cryptographic verification. The intended defense did not exist, or did not work as believed.
This is important to state precisely. Most exploits in crypto target humans or processes: a password stolen, a device left on, a code deployment that left a port open. If you fix the endpoint, you "fix" the system. Here the issue is different. The entire system trusted an assurance — "L-BTC is only minted against real bitcoin" — and that assurance failed at the cryptographic level. Not just a wrong configuration; a category mistake about what was guaranteed.
This breach did not require the attacker to go through a long social chain. There was no admin who missed an email alert, no over-permissioned server, no unlocked building. The attacker found a way to convince the sidechain to create almost 4,000 L-BTC that should not have existed, by defeating the core cryptographic check. If the proof-of-peg can be faked, possession of the underlying asset evaporates into opinion.
Had this happened on Ethereum mainnet, the outcry would have broken every analytics dashboard and funding channel at once. Instead, most users treat it as a thing that happened elsewhere, to other people, in a parallel system not directly connected to their funds.
What a Sidechain Is — and Why Security Claims Usually Fail
A sidechain is not just another app chain. It exists to move assets from a proven base-layer (like Bitcoin) to a faster, cheaper or feature-rich environment, with the promise that the asset can always be redeemed on the originating chain at the same value.
The process is supposed to go like this:
- User locks an asset (BTC) in a contract or with a federation of custodians on the base chain.
- The sidechain issues an equal amount of "wrapped" or pegged asset (L-BTC) to the user or destination address.
- When the user wants to leave, their wrapped asset is burned on the sidechain and the corresponding BTC is released from lock on the base chain.
Security, in theory, is assured by cryptographic proofs or by multi-party custody: the sidechain contract cannot mint wrapped tokens without the real asset being locked and cannot release locked funds without proof of burn. In practice, there is a spectrum:
- Some sidechains use federations: a set of signers who collectively authorize mints and burns, distributing trust but not eliminating central points.
- Some use SPV (simple payment verification) proofs or zero-knowledge proofs: more robust, but technically complex and hard to implement without holes.
- Some are just trusted custodians with a UI.
The Liquid hack exposed the limit here: if the bridge between chains is cryptographically insecure, the wrapped asset is only as real as the weakest link in that bridge. You do not have BTC; you have a claim on a process that might be vulnerable in ways that are invisible until too late.
If this is true for Liquid, what is the status of every other bridge or sidechain with less scrutiny and smaller budgets? The evidence says most users do not differentiate, because the flows did not change.
On-Chain Flow: What Ethereum Users Actually Did
The week’s net ETH flow is 2,669, bullish but not aggressive. Whale stance is 58% bullish. Not a rush, not a drain. If the Liquid exploit had pushed ETH holders to mass self-custody, I would have expected to see a clear spike. We did not. The Greed score is 61, which says the mood is still risk-on.
Here is what would have been different if the risk had landed as a genuine threat to Ethereum users:
- Sharp increase in exchange outflows: wallets pulling ETH to cold storage, looking to get outside possible counterparties' risk.
- New address activity: not just a few new wallets, but visible address creation clusters on Etherscan, wallets being diversified for firebreaks.
- Gas price spikes: panic consolidates transactions.
None of that showed up. The data reflects attention, not action. This fits a pattern: sidechain failures rarely move the base-layer holders — until the next exploit lands closer to home.
Why Bitcoin Sidechain Exploits Don't Move Ethereum
There is a reason for this indifference. Most of the base-layer holders treat each chain as logically separate: a Bitcoin sidechain hack is a "Bitcoin problem" unless it involves protocols that directly bridge to a chain where funds are held.
The on-chain mood matches this. Trezor’s incident — a breach at its email provider — did not trigger visible activity in either direction. Ethereum ETF flows, by press accounts, remained resilient; Bitcoin ETF products saw $460 million in outflows. On the chain, whales are accumulating ETH, not selling into perceived system risk.
The psychology is plain: users compartmentalize, correctly or not. They believe mainnet is insulated. This reading is at least rational: if your ETH is not bridged, someone forging L-BTC on the Liquid sidechain should not be able to touch your funds. But what is worrying is that they treat every sidechain as unconnected, until it is not. Most cascading failures do not look urgent until asset holders discover which “segregated system” is actually a hinge.
The Real Sidechain-Base Layer Divide
The split is bigger than risk; it is cultural. Ethereum base-layer holders and protocol-native funds operate with a mental firewall: off-layer risks are "interesting" but not treated as urgent. Even when bridge exploits have erased billions in bridged tokens elsewhere, you see flurries of concern, not mass movement — until the day someone finds that so-called mainnet was exposed through a dependency.
If the entire ETH ecosystem shared exposure to the vulnerable process seen in Liquid, the flows would have drawn bright lines. What happened instead? Nothing. Flows do not lie about urgency.
Strongest Objection: Aren't Most Users Just Smart About Segregation?
The opposition argument is clear: experienced holders, especially whales, isolate high-value funds on the base layer, and limit exposure to bridges and sidechains exactly because they know the risks. If ETH whales did not move, the claim runs, it is because they are not exposed. The system is working.
This has some support. It's possible major ETH holders weren’t directly exposed to anything in Liquid or to the mechanisms mirrored in Ethereum bridges. Prudent self-custody is not just holding coins; it is knowing not to leave them at risk in immature protocols. Maybe the discipline is real, and the calm on-chain data is evidence of a user base who learned from past failures.
But this answer is too simple and gives too much credit. There are always some sophisticated users who diversify; there are also asset pools, DAOs, and protocols that leave funds sitting on bridges and sidechains because yield and convenience talk louder than theoretical risk — until losses crystallize. Grouping all non-action as "well-managed exposure" is naïve.
If the only sidechains that matter are the ones already capitalized with ill-informed money, that is no comfort to the market. The distinction between “the sophisticated whales do X, the rest do Y” misses that most custody choices are made by inertia, not analysis. And protocol-level bridges are built on the premise that systemic risk management lives a level above the whale wallet. That premise just broke, in Liquid, on-chain.
Second Mechanism: How Bridges Actually Fail
There is a hidden risk in assuming “not my chain, not my problem.” Tokens flow between chains through smart contracts, federations, or custodians that are often under-audited. When a bridge acts as a mint-and-burn ledger, it must guarantee:
- Peg: New tokens minted only if the asset is truly locked on the other side.
- Integrity: No admin, keyholder, or script can override the peg.
- Availability: Withdrawals always possible for pegged tokens.
If the proof fails—if a script is wrong, a signer is compromised, or a cryptographic primitive was misapplied—you get phantom collateral: tokens existing without real backing. Panic lags until the exploit spreads, then everybody exits at once, and only the first out get real redemption.
The mechanism exposed by the Liquid hack is not just a simple coding bug, it is the core check on existence and solvency. When that fails, every assumption collapses. If even Bitcoin’s largest sidechain can fail like this, there is no reason to believe smaller or more experimental sidechains are safer.
Why Custody Still Reverts to Habit
Almost every time I’ve seen a bridge or sidechain breach, the biggest wallets live by the iron law of crypto psychology: “It’s not my risk, until it is.” On the rare weeks that fear breaks through, the numbers are obvious — outflows double or triple, new addresses spike, gas goes up. This week, that did not happen.
Why? There are two honest readings. One: the user base knows the risks but chooses to prioritize yield, speed or flexibility. Two: the abstract nature of “sidechain risk” is easy to ignore compared to a phishing attack or a platform rug. I lean toward the second. Sidechain security is still seen as external — until it is not.
For a sidechain breach to shift user behaviour, one of two things needs to break: the separation between the affected chain and assets people care about, or the illusion that mainnet cannot be touched by off-layer errors. So far, neither has happened in a way that became personal for ETH whales.
What Would Change My Mind
If next week brings a breach on a major bridge with demonstrable outflows — not 2,669 ETH net, but a multiple of that, with Tureng addresses lighting up on Etherscan — I would have to admit that user behaviour is shifting. Another signal would be a sharp drop in the Greed index, fast enough to register against the backdrop of this week’s 61. I do not expect it unless the next failure is bigger, closer, and unambiguously traced to a mainnet protocol.
A protocol-level exploit, or a bridge that serves as critical infrastructure between layers, is the real test. Until then, most action is lip service, not capital moving.
What to Watch Next
I am watching for three things:
- Any sharp spike in outflows from exchanges, not just on Bitcoin but on Ethereum.
- A shift in whale stance from soft bullish to defensive.
- Wallets moving in clusters: many addresses with new creation dates and transfers in a tight window, as when fear finally hits.
So far, each breach reads as the last breach: another proof that second-layer custody is years behind mainnet security, and user action still lags until pain is personal.
If your approach is to keep keys cold and activity isolated, as Siade Whales enables in a privacy-centric toolkit, this is another reason to stay cold, not complacent. https://siadewhales.com